Cross App Access Demo
Cross App Access is an OAuth extension that enables an enterprise IdP to manage the OAuth connections between applications.
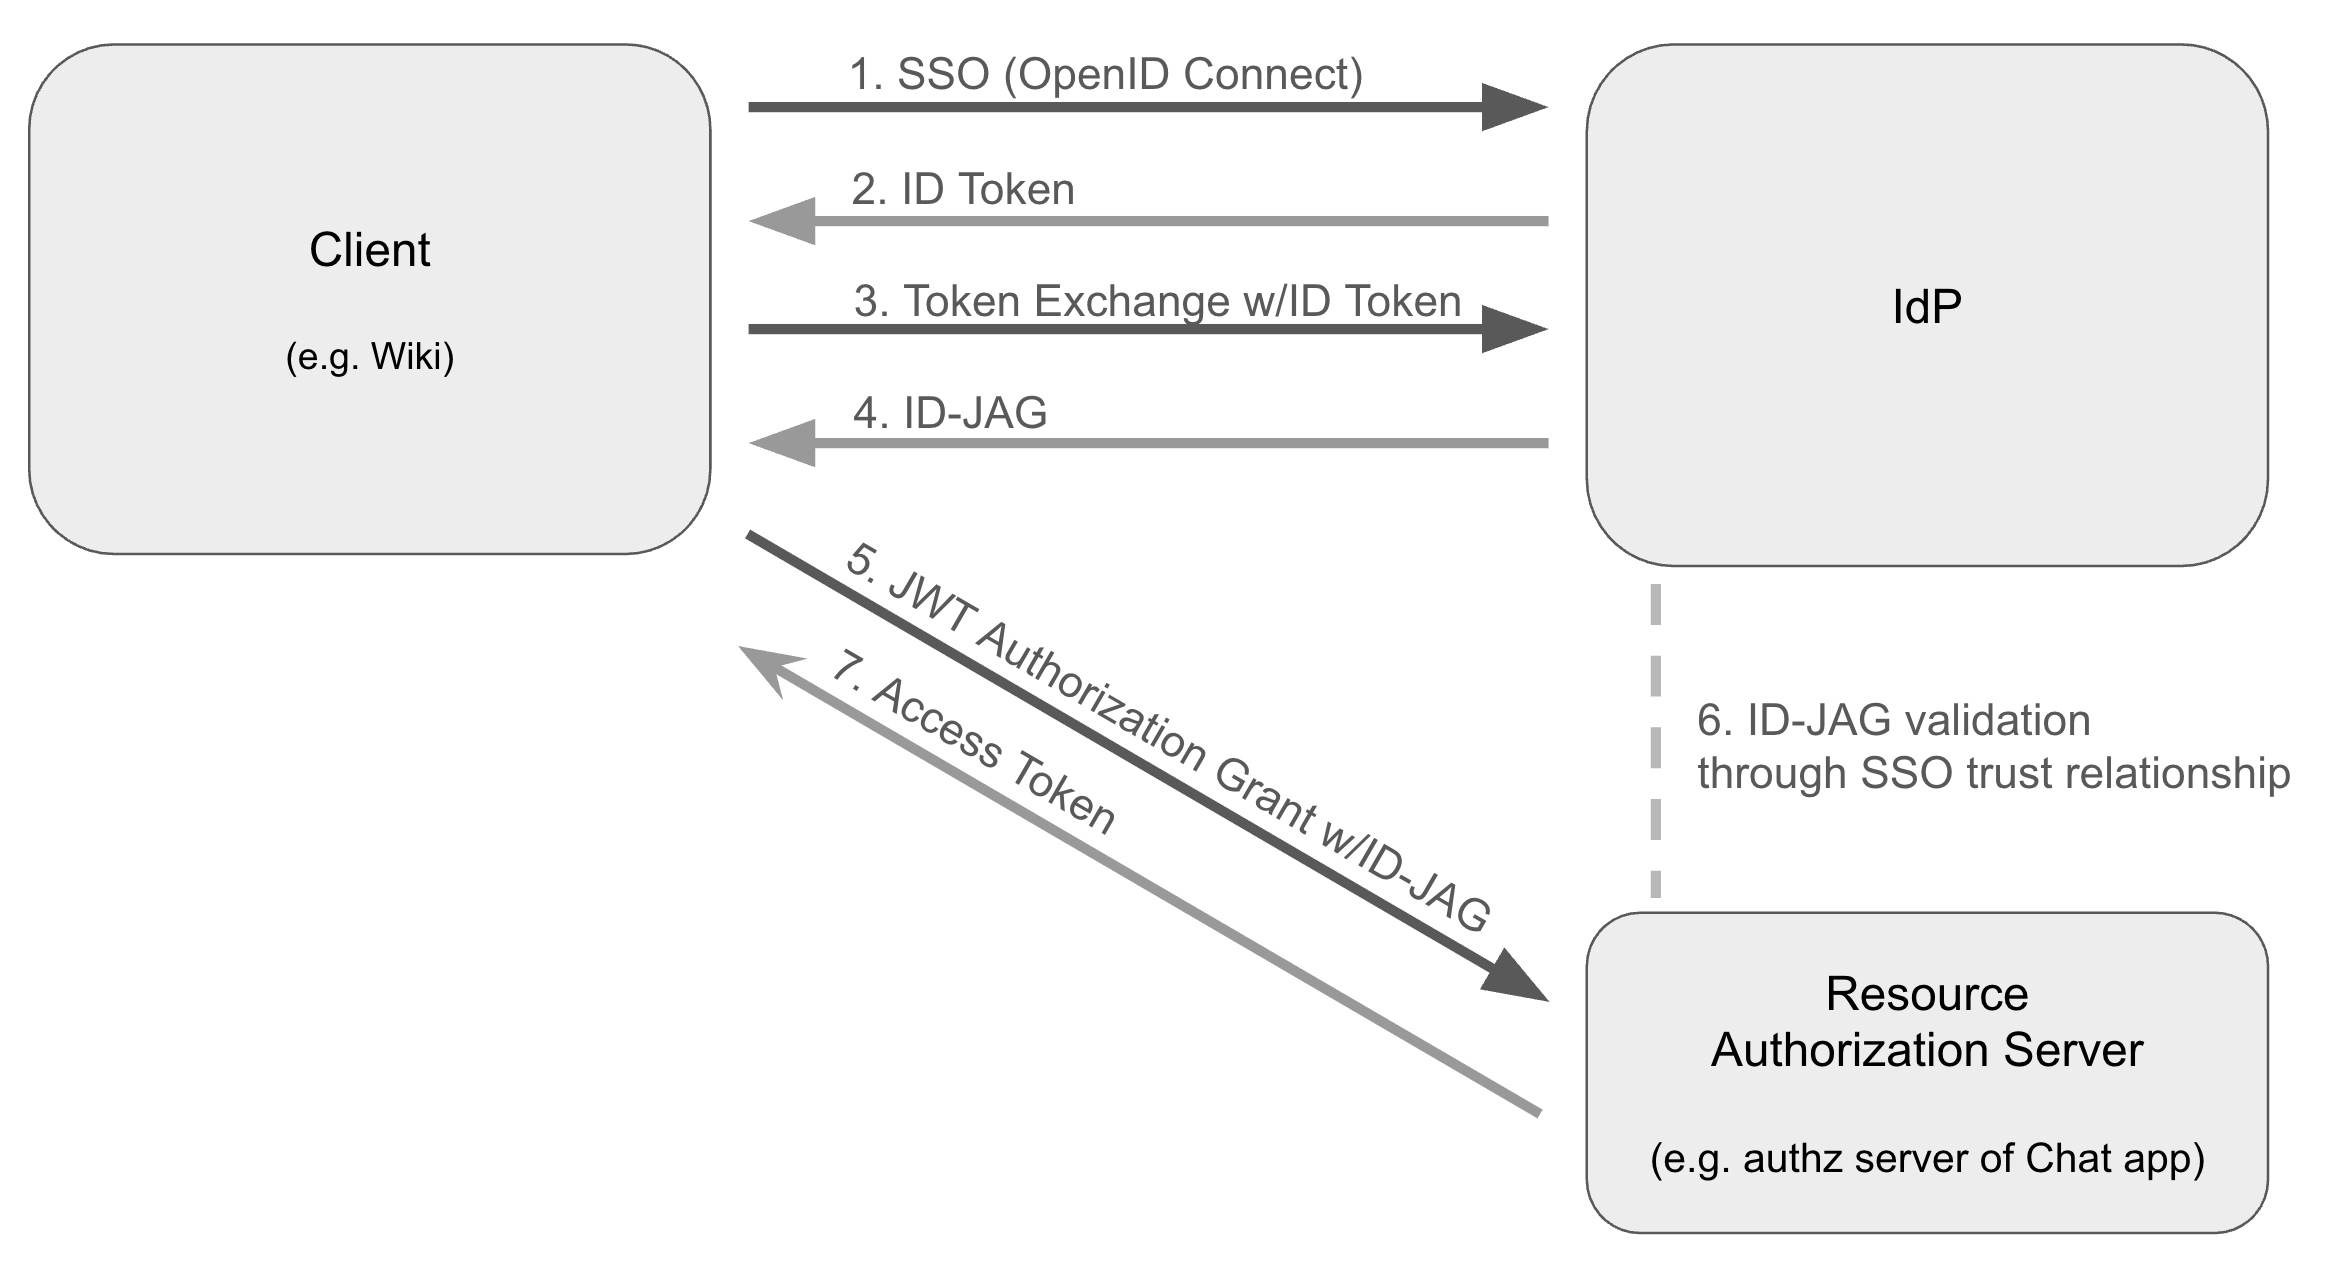
Endpoints
This website acts as a Resource application. You can use it to test out building a Client. As a Resource application, it includes both an internal Authorization Server as well as a simple API.
- Token
-
https://motd.xaa.rocks/tokenIssues access tokens when presented with a valid ID-JAG
- Message
-
https://motd.xaa.rocks/motdWhen presented with a valid access token, returns the message of the day
- MCP
-
https://motd.xaa.rocks/mcpYou can connect to this MCP server to retrieve the message of the day via MCP
Try it
-
Configure your IdP to issue ID-JAGs with an
audiencevalue ofhttps://motd.xaa.rocks/ - Sign in to your Client through the IdP
- Make a Token Exchange request to your IdP to exchange the ID Token for an ID-JAG
- Make an Access Token request to this website to exchange the ID-JAG for an access token
- Make a request to this website's
motdendpoint to find the daily secret message
Any issuer is accepted.
This website will accept ID-JAGs from any issuer for demonstration purposes. In practice, a SaaS
app like this will likely restrict the issuers it accepts ID-JAGs from to enterprise IDPs of
current customers.